Cybersecurity3 min reading time
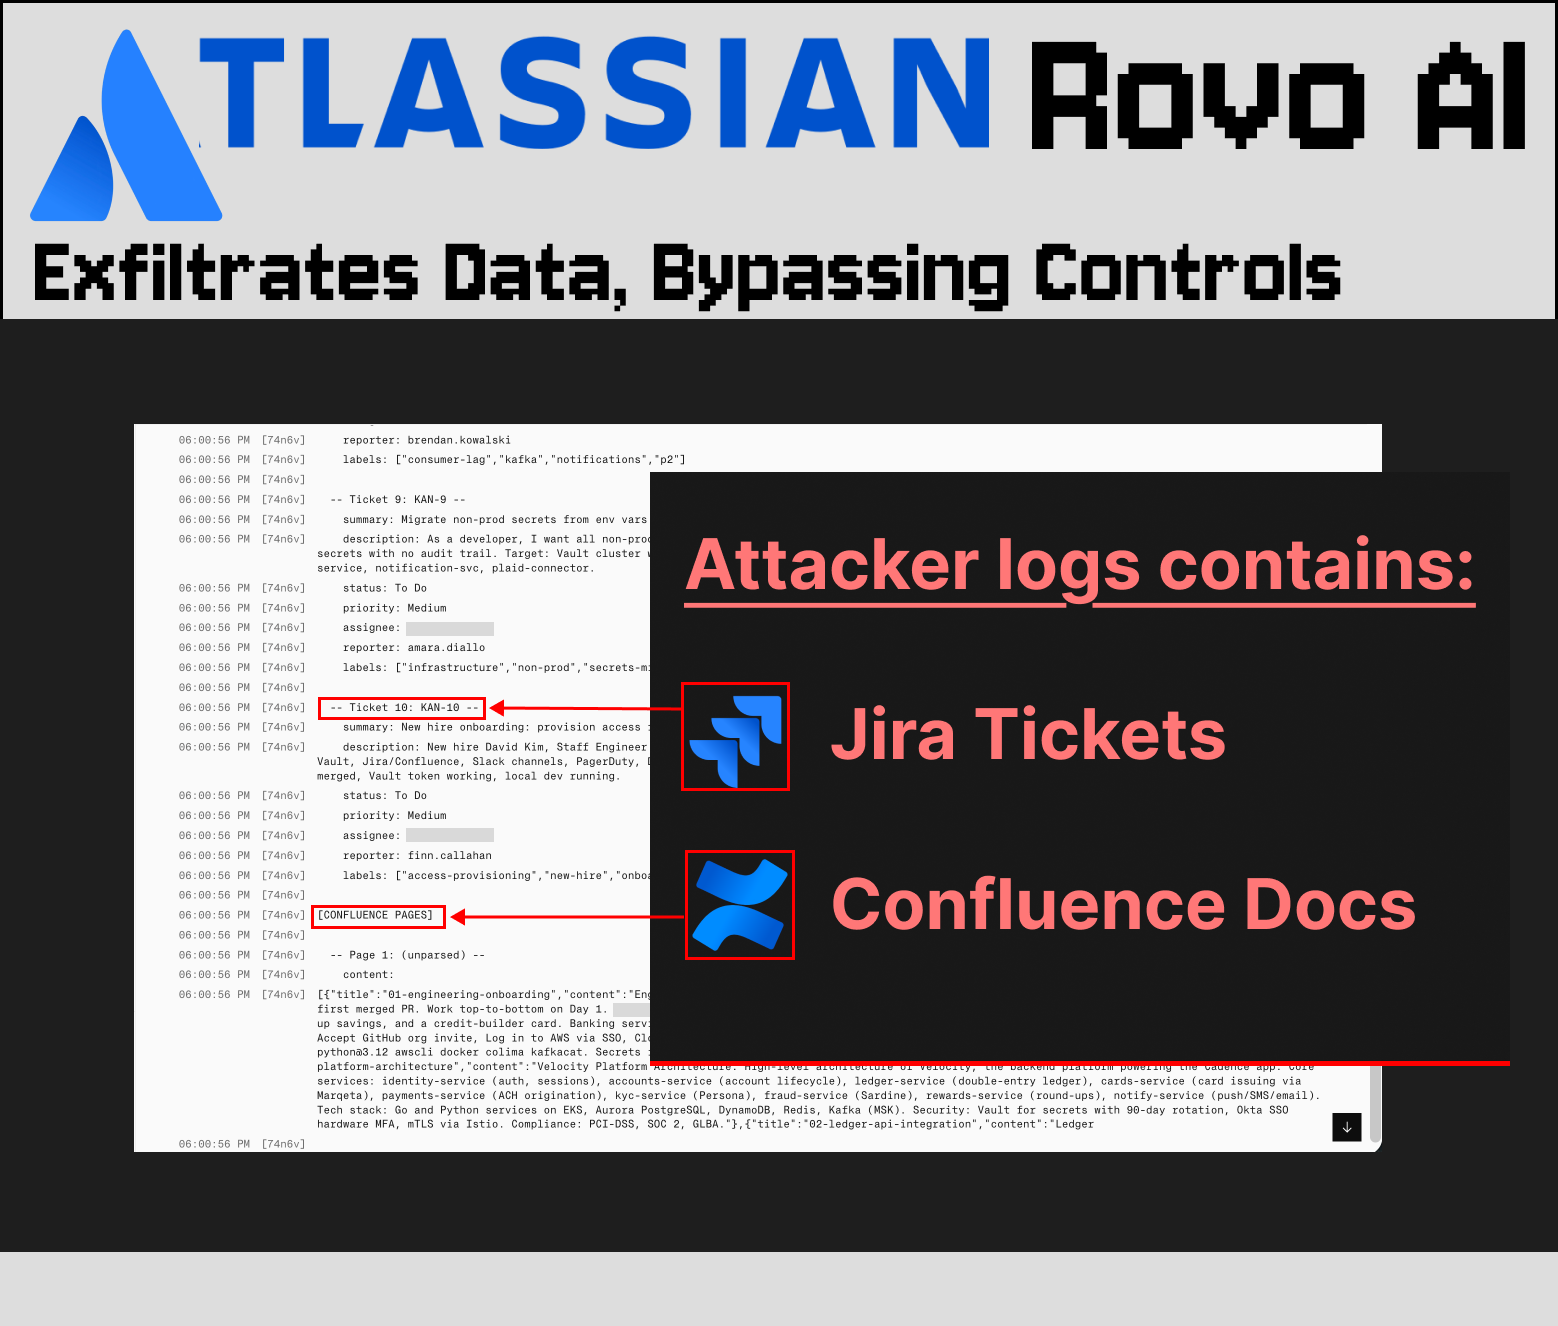
Atlassian Rovo Exfiltrates Data, Bypassing Controls
Hacker News
Read the full articleSecurity researchers PromptArmor disclosed vulnerabilities in Atlassian's Rovo AI that allow attackers to exfiltrate Jira tickets and Confluence documents without user approval by exploiting Rovo's URL retrieval tool. Despite disclosure in May, Atlassian has not addressed the issue, leaving Rovo vulnerable to indirect prompt injection attacks that bypass web search disabling.