

Claroc Research Finds 35,578 Grok Apps Accessible Without Sign-In
What happened
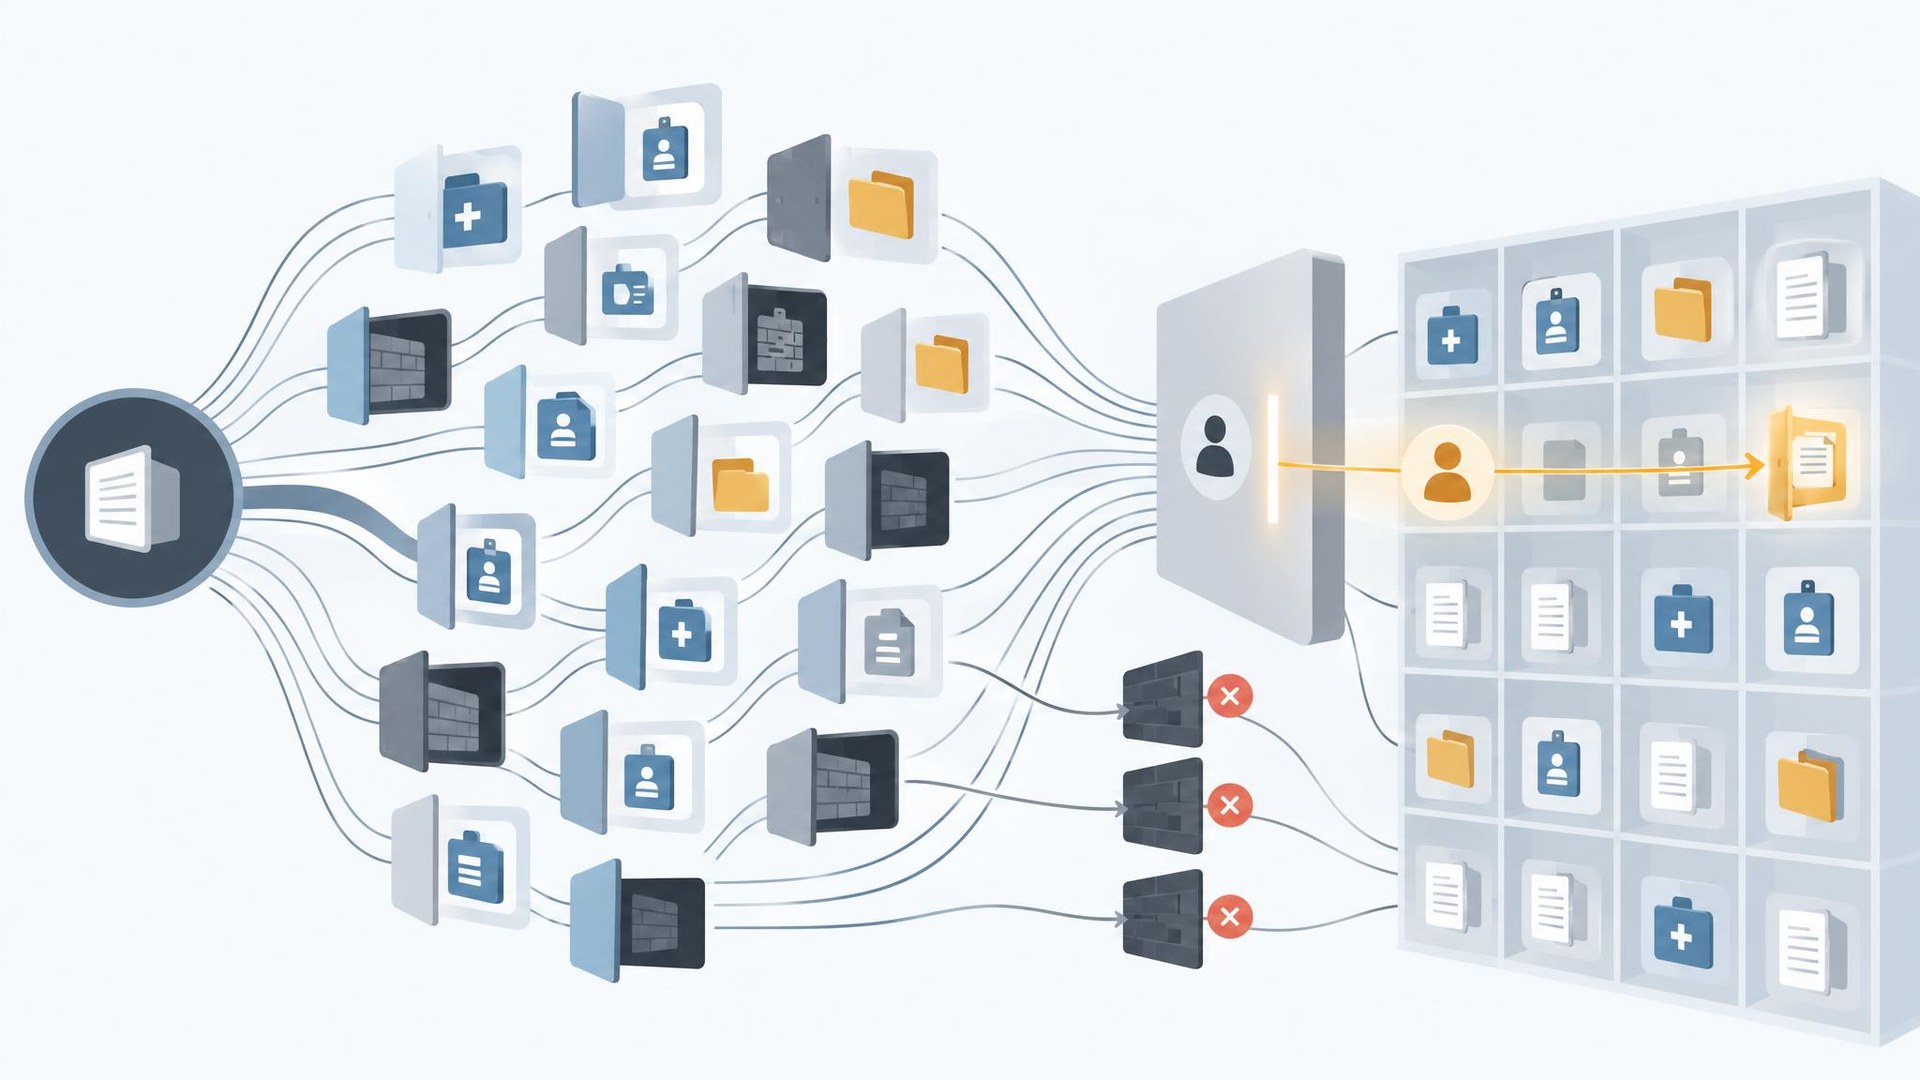
On November 10, 2026, Claroc Research reported that 35,578 Grok apps were accessible from the internet without requiring users to sign in. These apps included 24 created by staff at SpaceXSI and X, and many contained confidential business and personal information. Claroc found data such as sales plans, employee lists, patient information, and passwords in the open apps. Following the report, SpaceXSI staff apps were taken offline, but other exposed apps remained accessible.
Key details
- Claroc tested 37,571 Grok apps and found 35,578 open without sign-in.
- 24 of the open apps were built by SpaceXSI and X employees.
- 650 to 800 apps were estimated to contain private data, based on AI and manual review.
- Examples of exposed data included a hospital’s employee roster, patient records, and a contractor’s timesheet with plaintext passwords.
- Claroc notified SpaceXSI on November 8 and 9, 2026, and began contacting other affected organizations directly.
Why it matters
Organizations using Grok apps, including large companies and public sector groups, faced exposure of sensitive internal and personal data to anyone on the internet. This created risks of data leaks, unauthorized access, and potential misuse of confidential information. App creators and IT departments now need to review their Grok app settings and data handling practices to prevent further unauthorized disclosures.