

Cloudflare Develops Public Certificate Authority for Post-Quantum Web Security
What happened
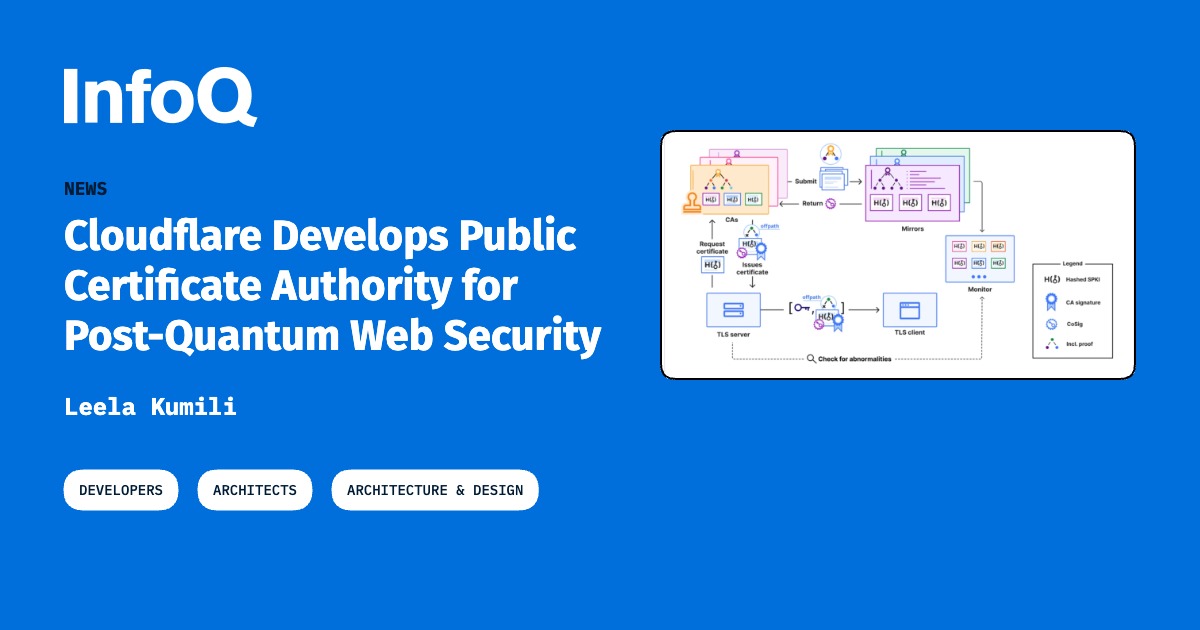
Cloudflare conducted an experiment using Merkle Tree Certificates (MTCs) in the Chrome Beta browser, serving billions of certificates to selected domains. The test achieved a 9% improvement in median performance by replacing traditional certificate chains with compact cryptographic proofs. The experiment ended in August 2026. Cloudflare is now developing a public certificate authority that will issue MTCs, aiming for inclusion in Chrome’s quantum-resistant Root Store in early 2027, pending evaluation.
Key details
- Cloudflare served MTCs to 50% of Chrome Beta 146 users for certain domains on its free plan.
- The experiment used classical cryptographic signatures, not post-quantum signatures.
- Post-quantum signatures can be about 40 times larger than classical ones, increasing bandwidth and storage needs.
- MTCs combine certificate issuance with transparency logging using an append-only Merkle tree.
- Cloudflare’s CA will need to pass evaluation before being trusted by Chrome’s Root Store.
Why it matters
Web users, browser vendors, and website operators are affected by the shift to post-quantum web security. The new certificate authority could reduce data transmitted during secure connections, addressing the challenge of larger post-quantum signatures. Website operators and browser makers will need to adapt to new certificate formats and verification methods as part of the transition to quantum-resistant security standards.