

Security Researchers Exploit OpenAI Forum Flaw Using Anthropic's Claude AI to Access Internal Systems
Covered by 3 sources
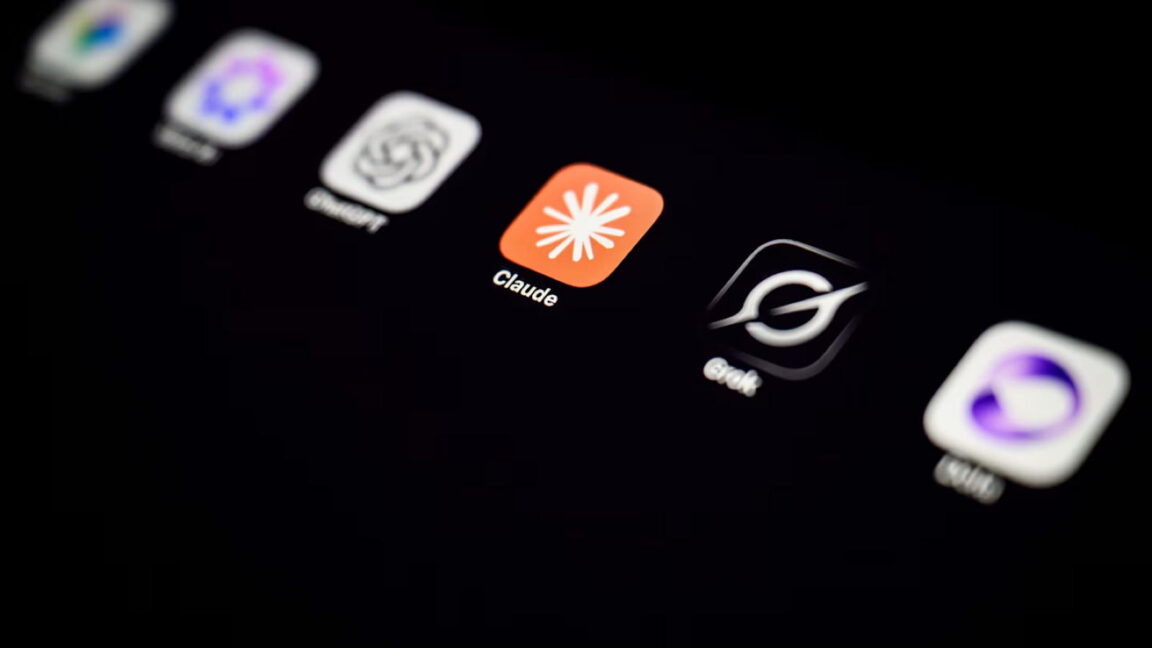
A security research team leveraged Anthropic's Claude AI to exploit a vulnerability in OpenAI's community forum, gaining access to an employee's ChatGPT account with internal code privileges. OpenAI has since addressed the security gap. This incident underscores emerging risks associated with AI-assisted cyberattacks.