How AI coding tools could amplify software supply-chain attacks
The Next Web
Read the full article
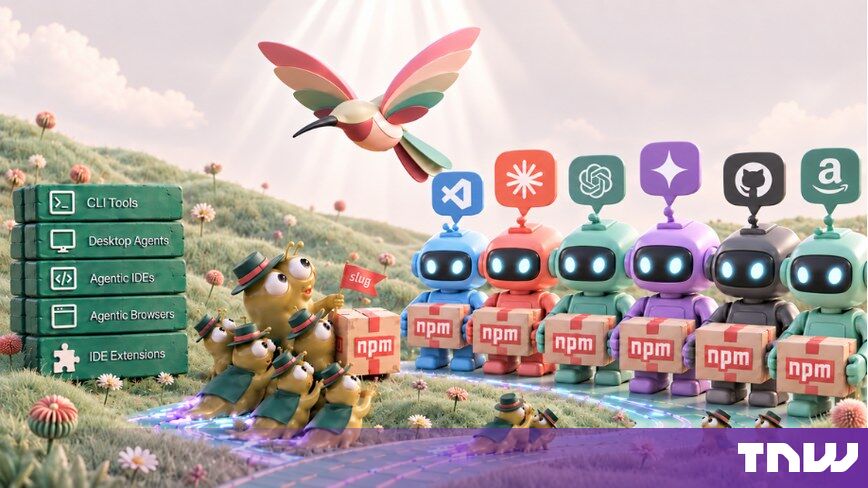
Bloom Security's research reveals that AI coding tools significantly increase automated software package installations, exposing enterprises to supply-chain attacks via vulnerabilities in npm package publishing. Over 1,500 npm packages with 10 million downloads are vulnerable, raising concerns about AI-driven dependency management and enterprise security risks.